Prove every control with signed evidence.
The guardian tests its controls every hour against six frameworks and packages the evidence auditors request into signed packs they can verify independently. The guardian provides the evidence; compliance determinations remain with your auditor.
Audit evidence for every framework in one console.
Control tests, framework mappings, evidence, access reviews and auditor workspaces, all built from the records the guardian already keeps.
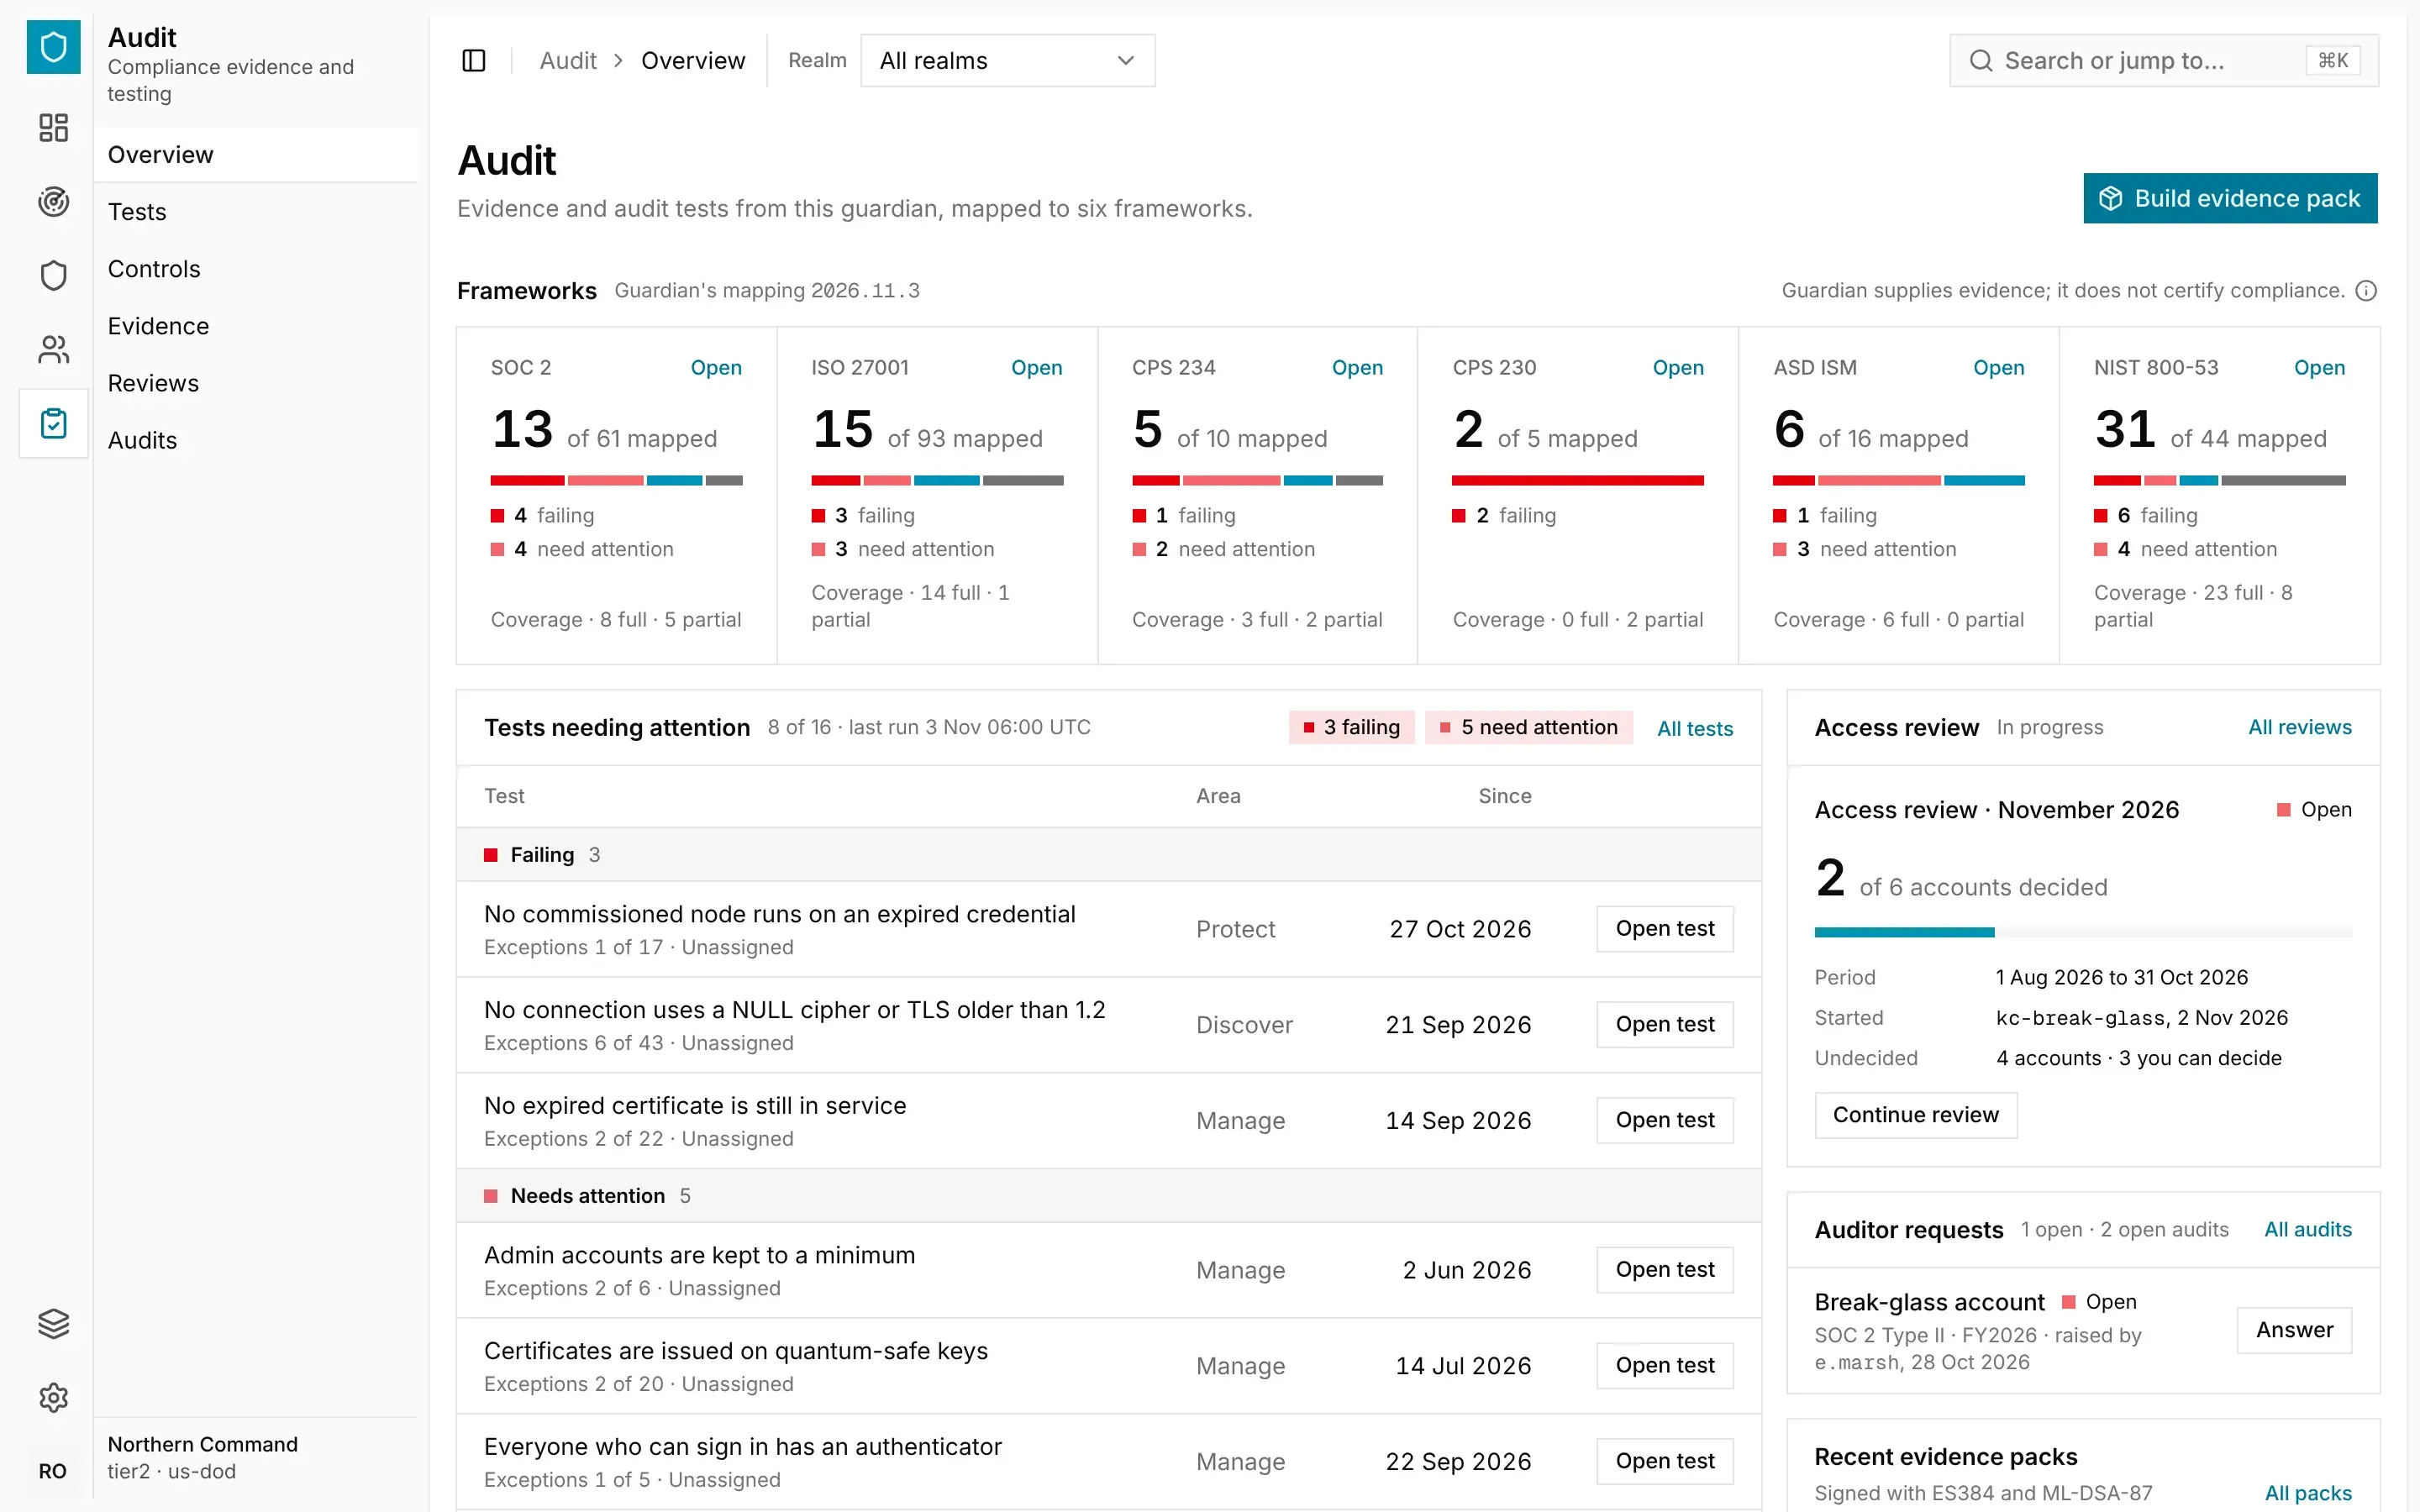
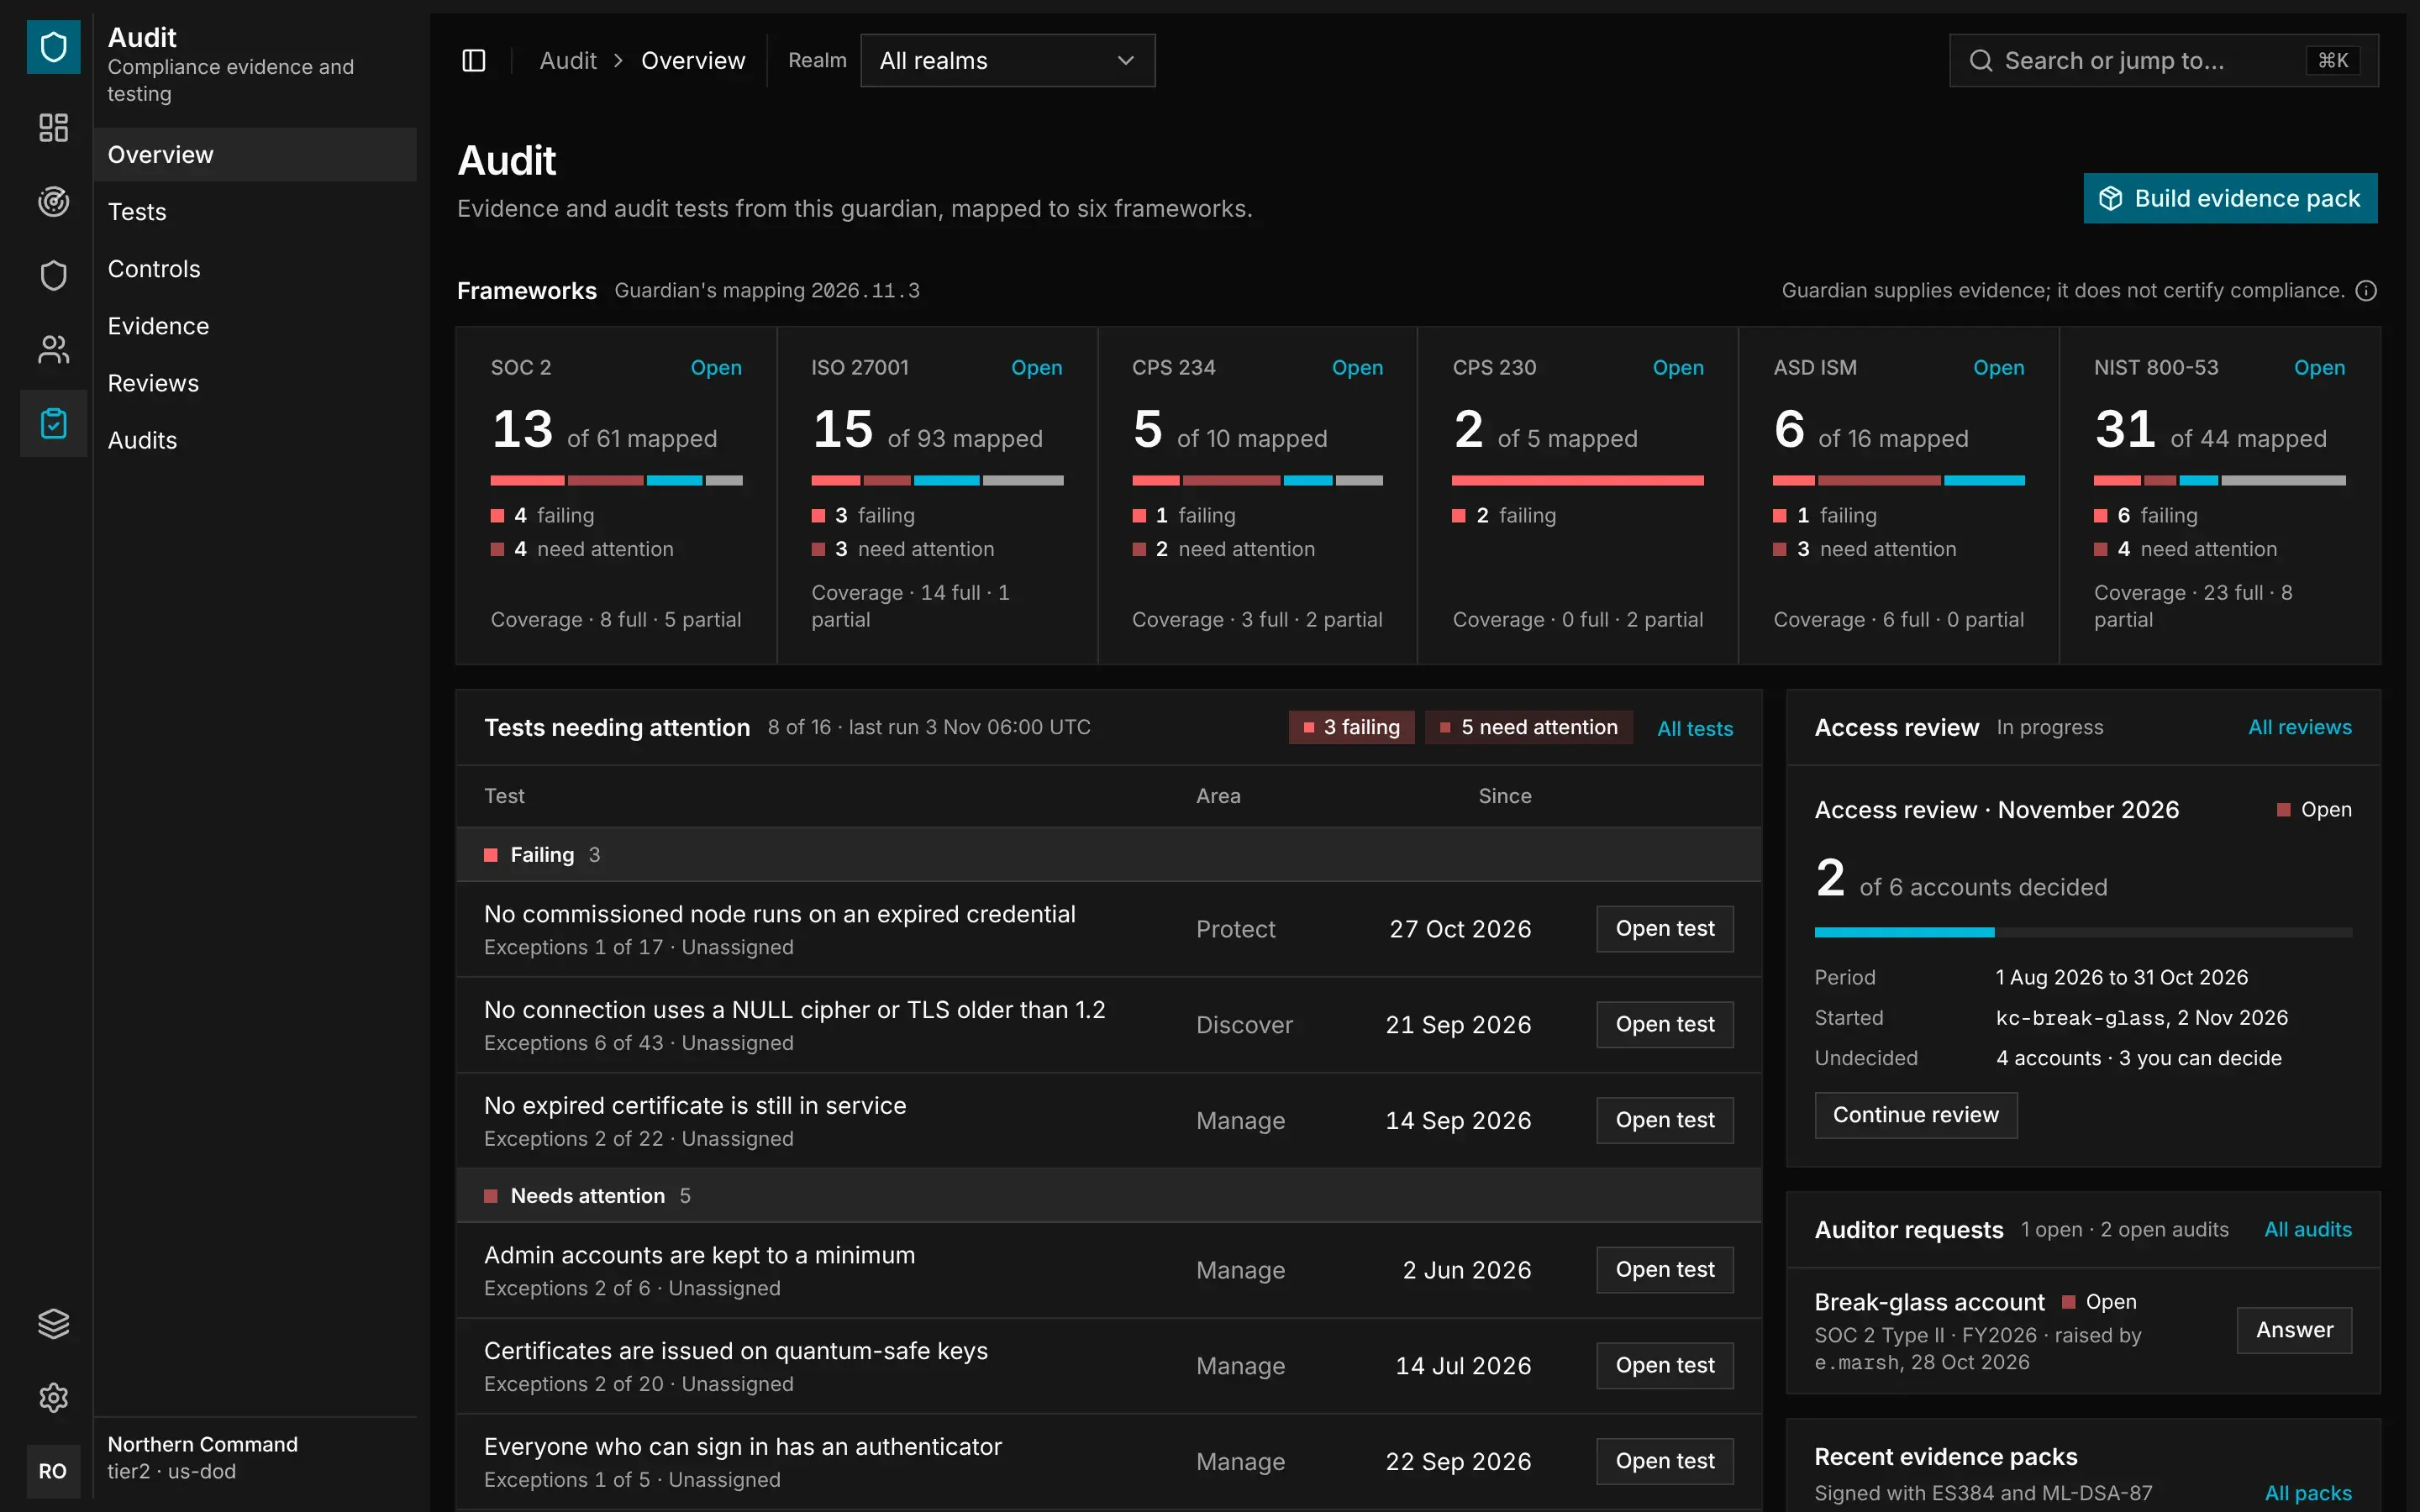
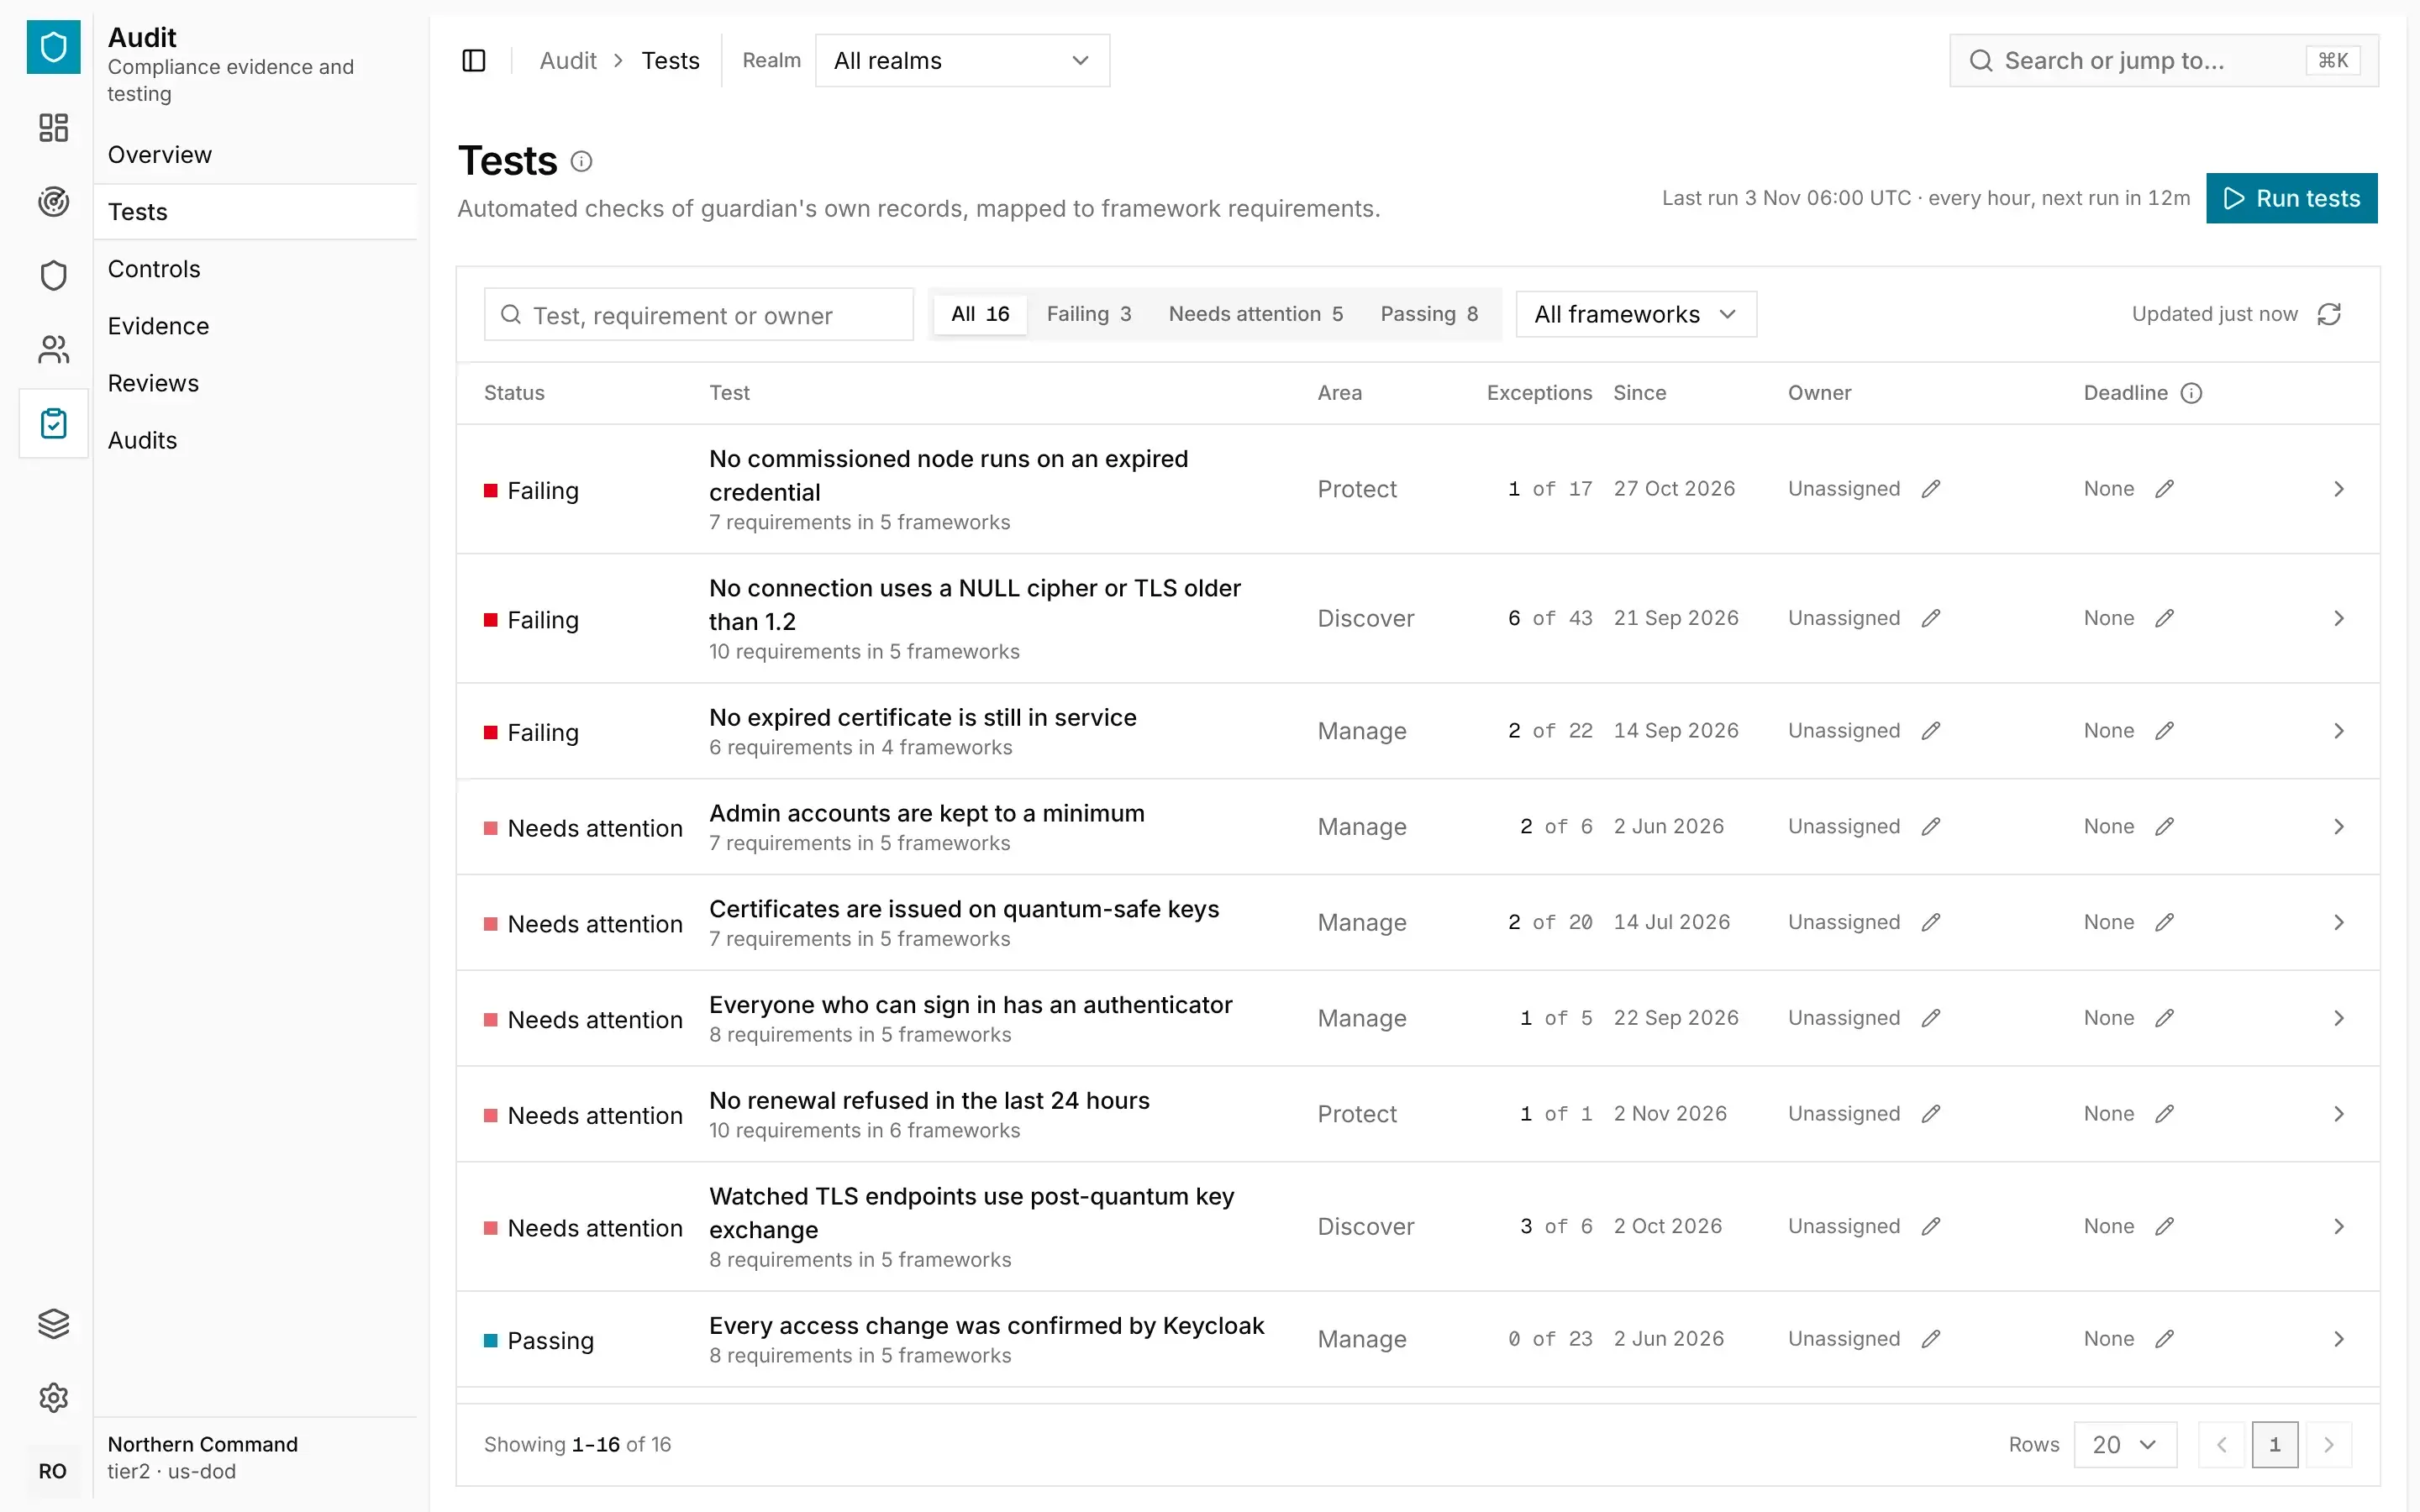
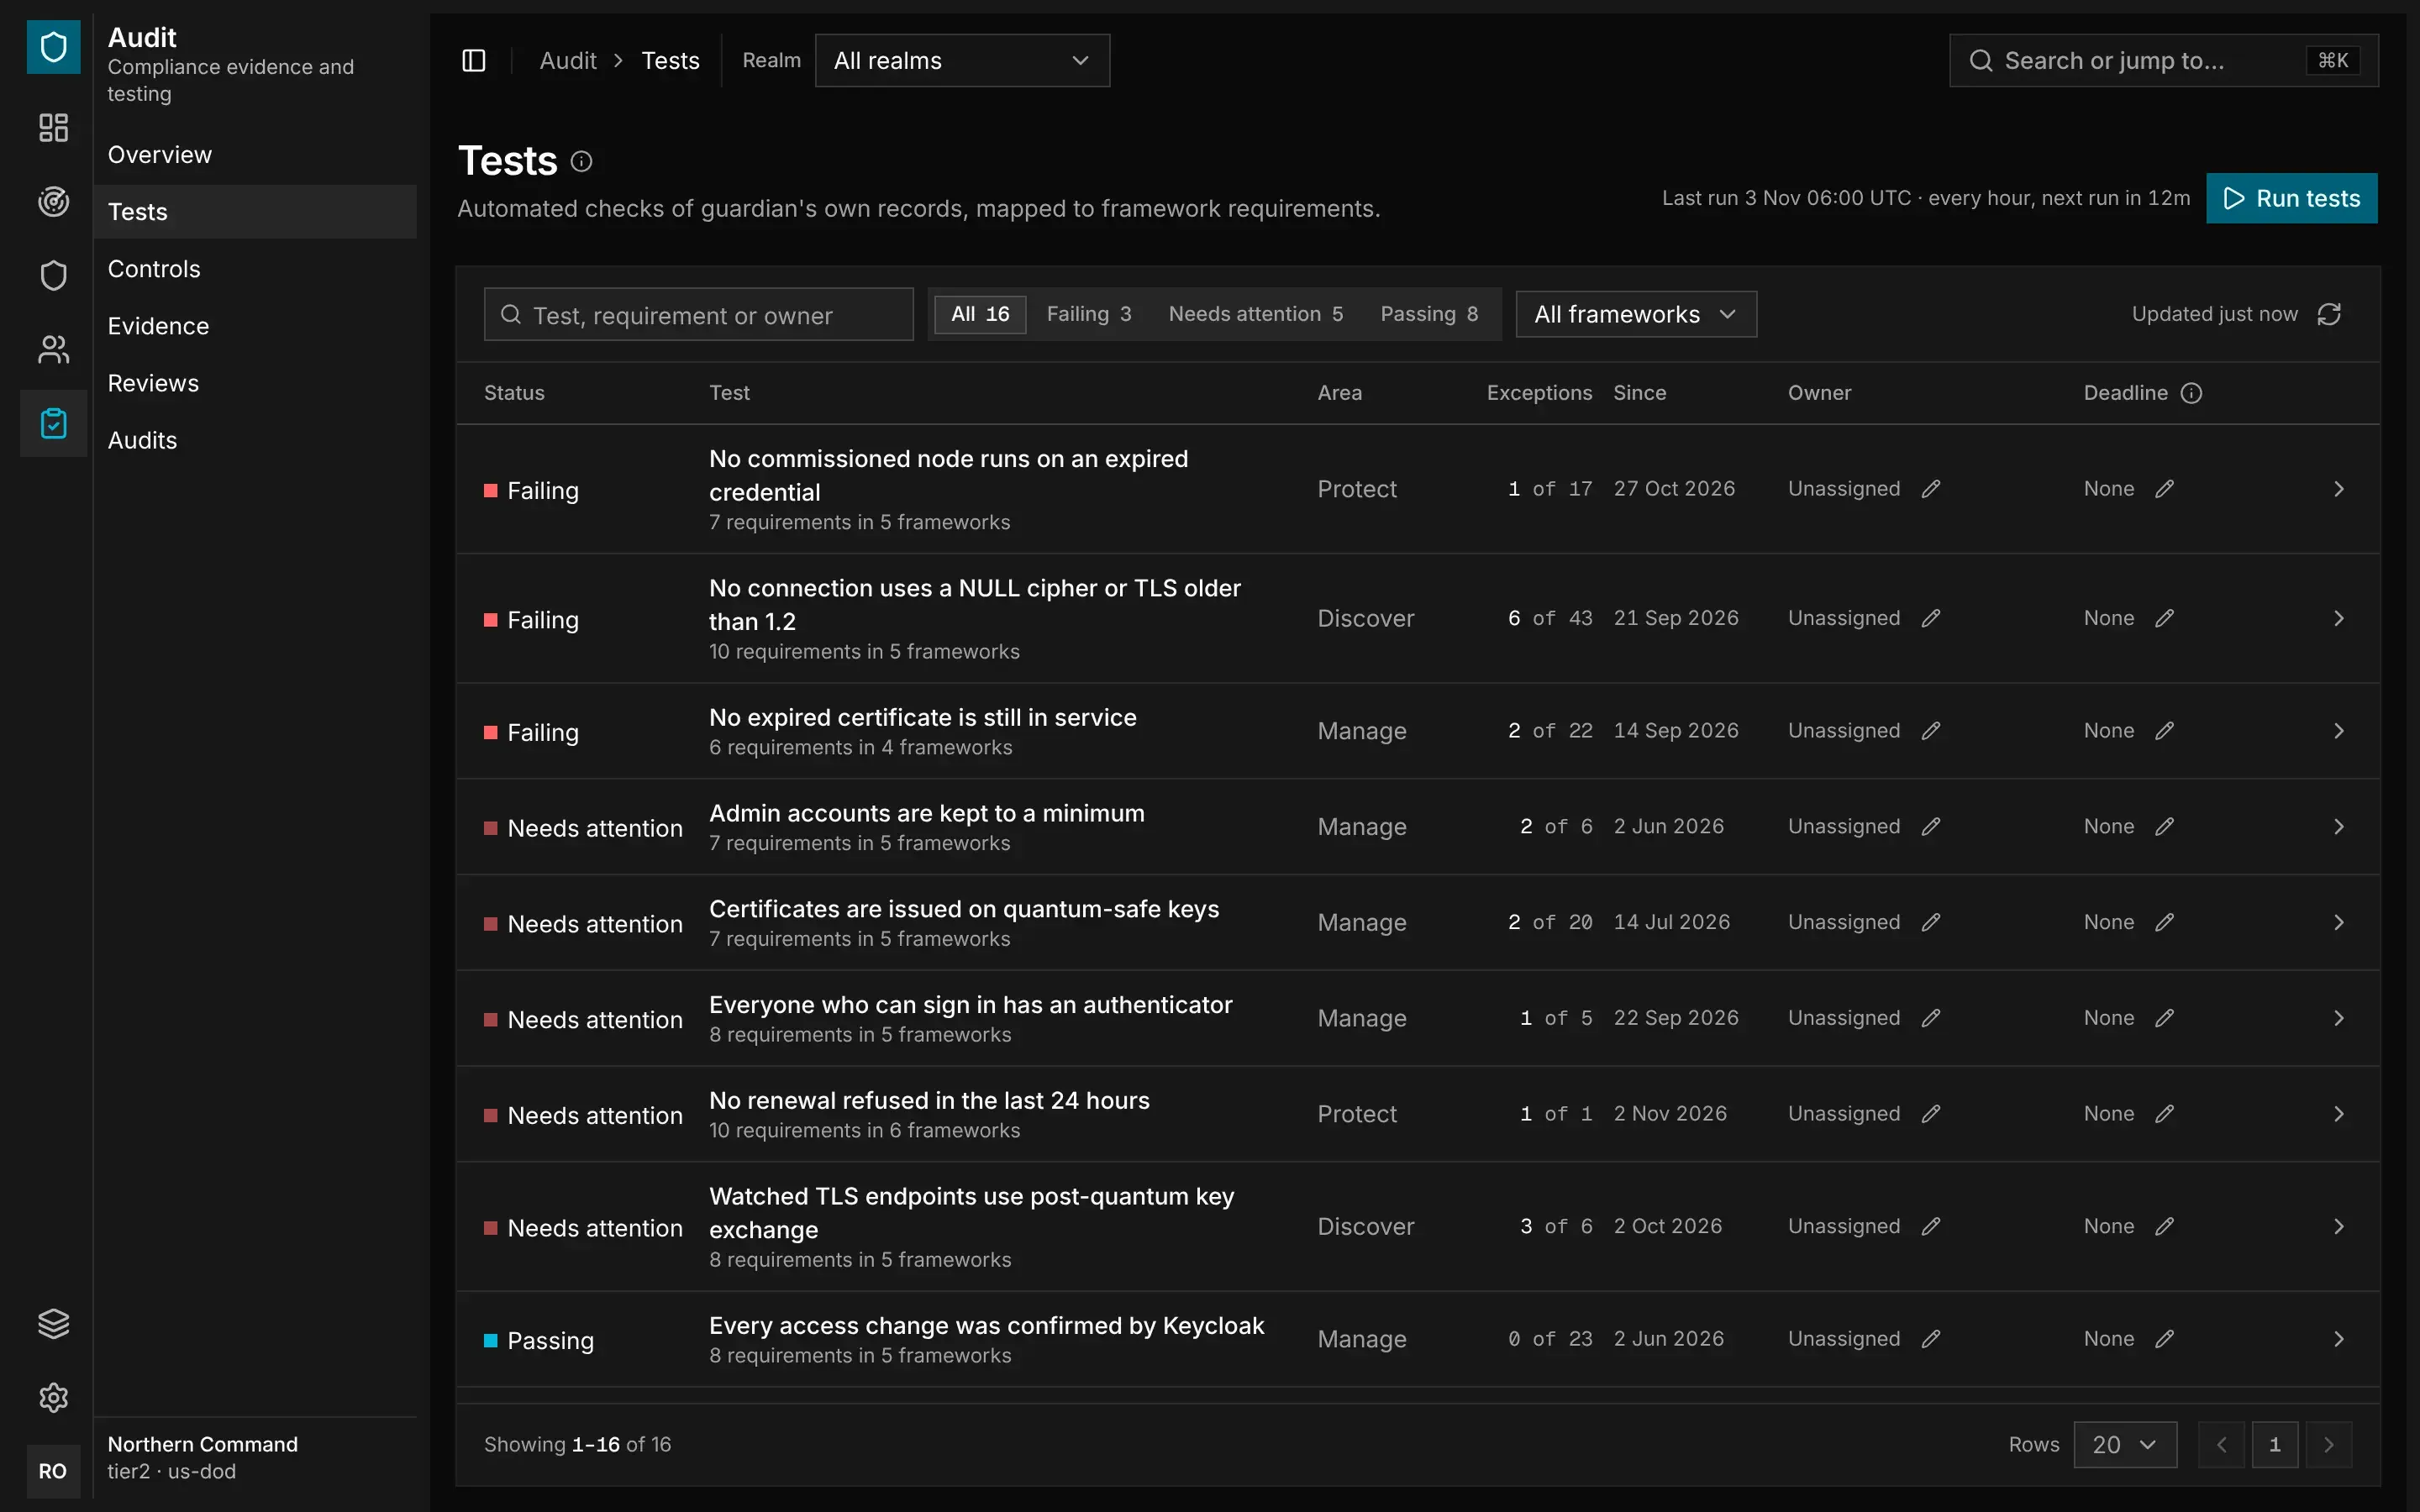
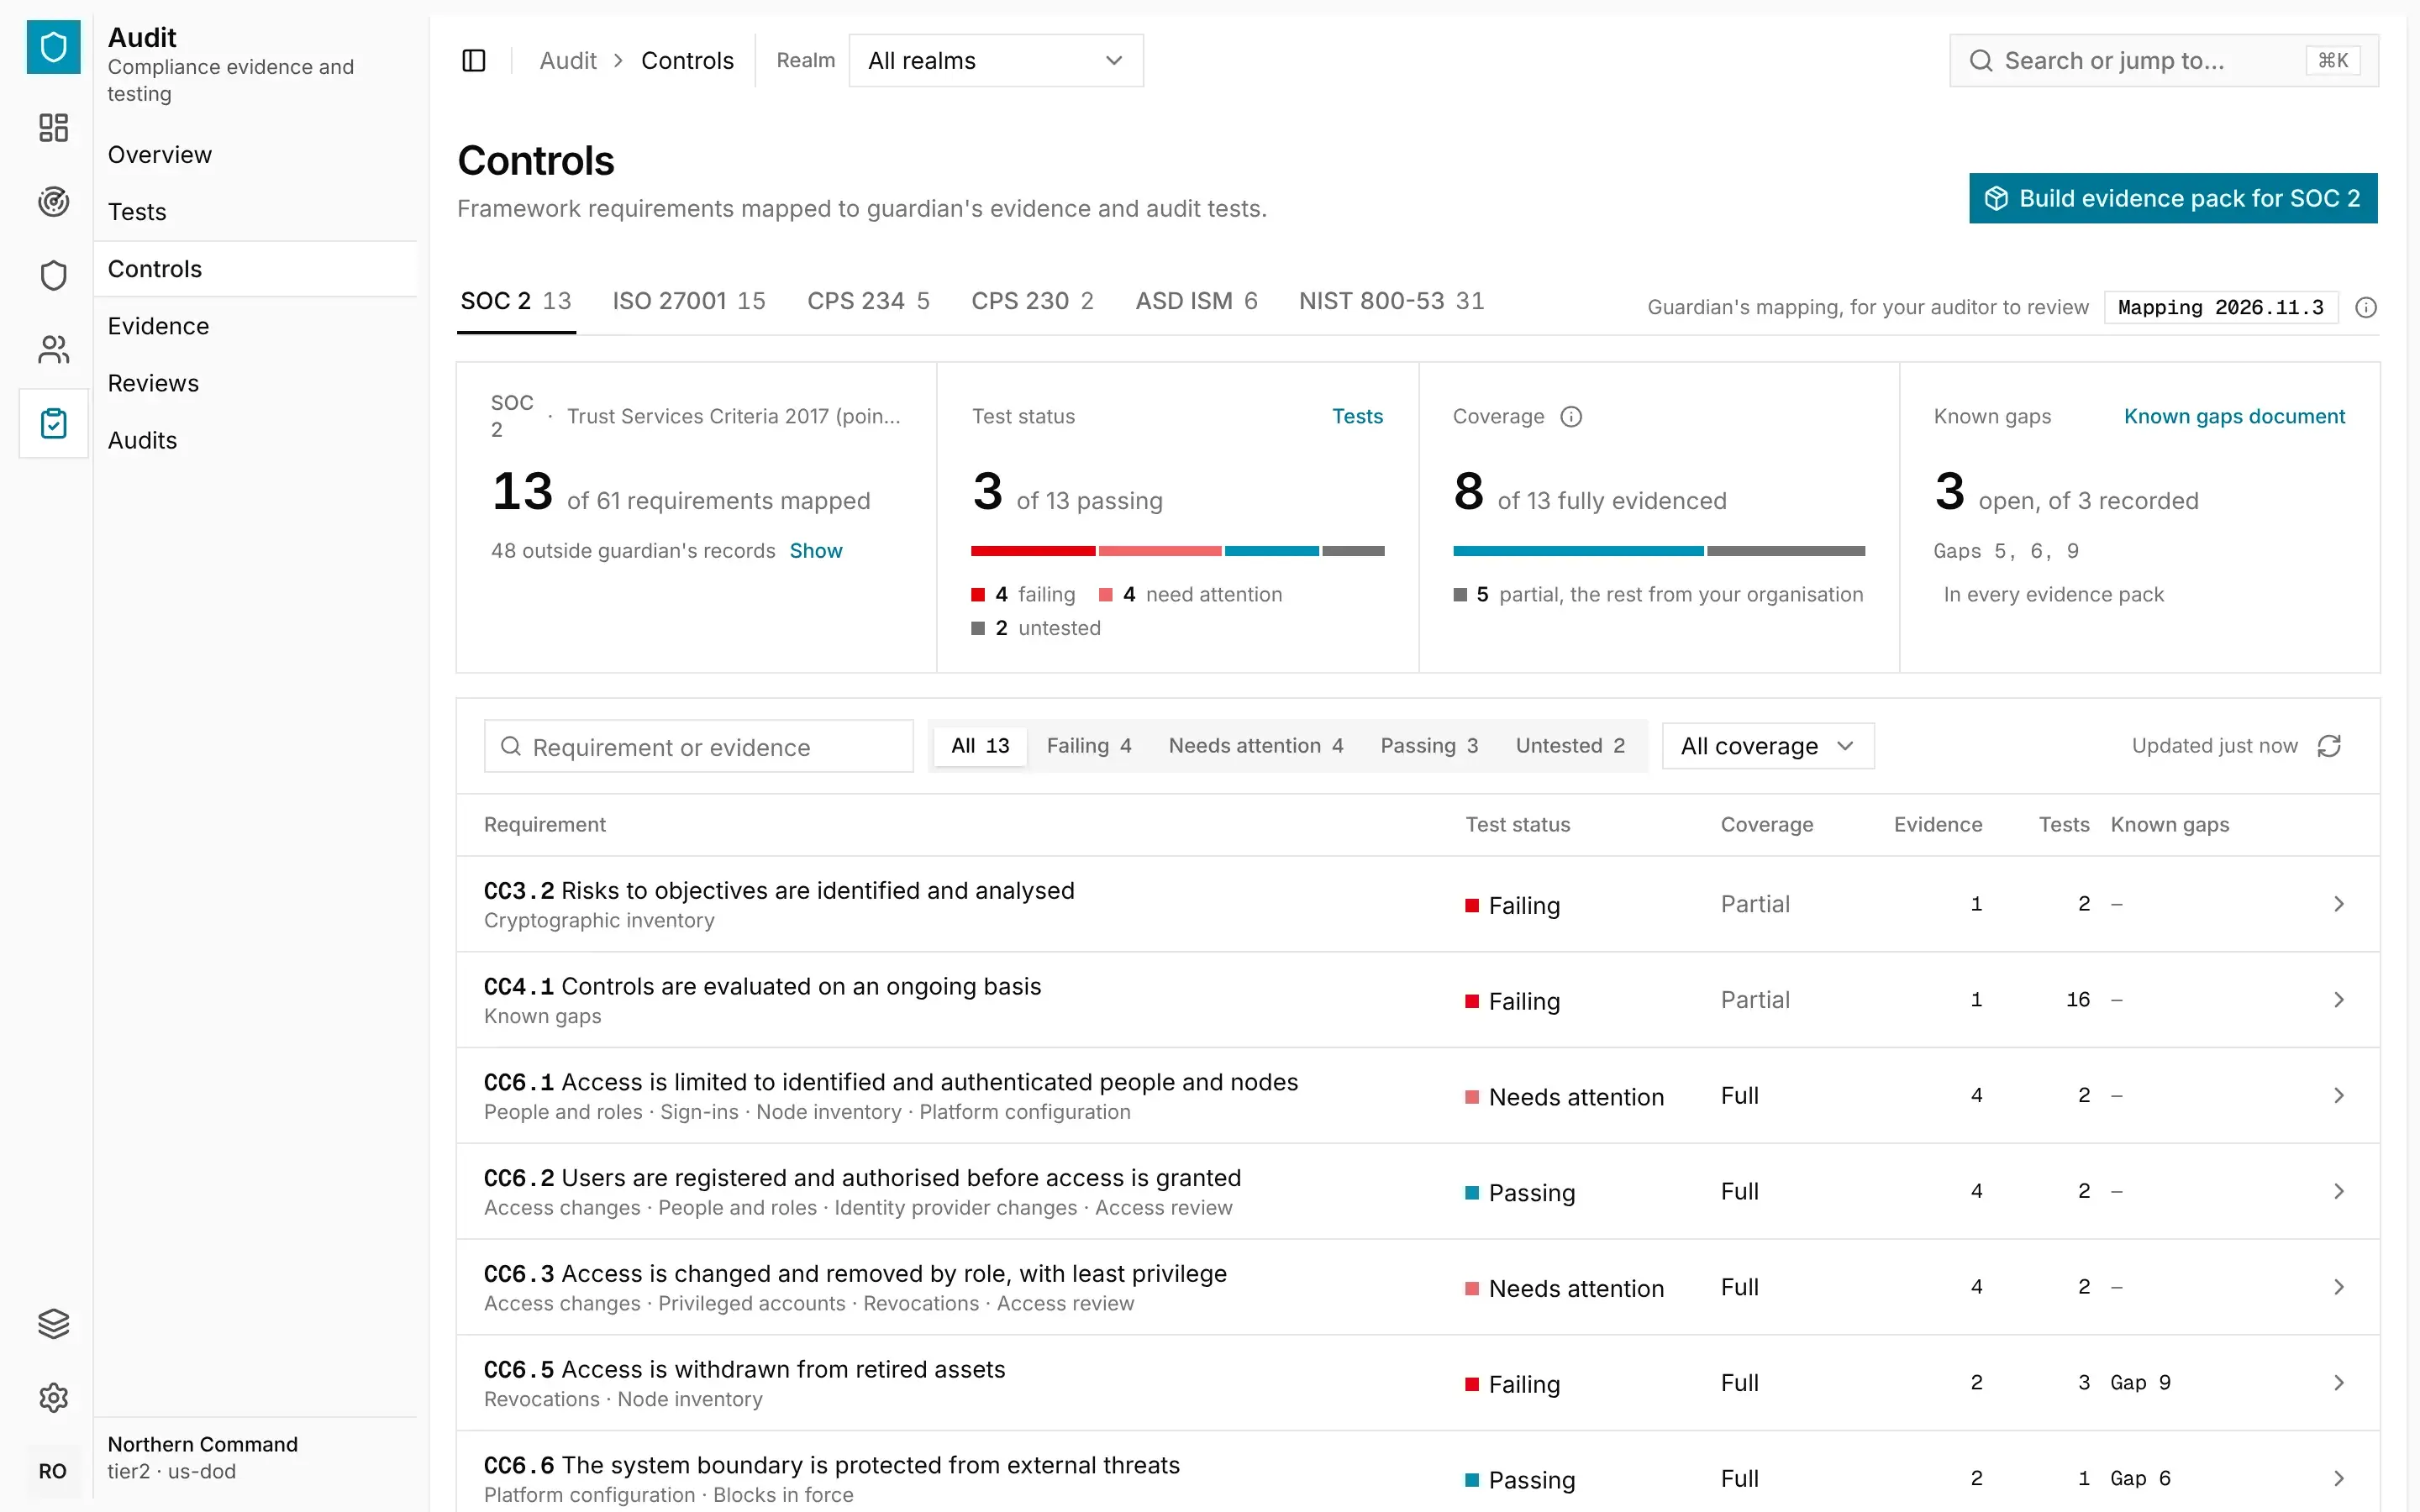
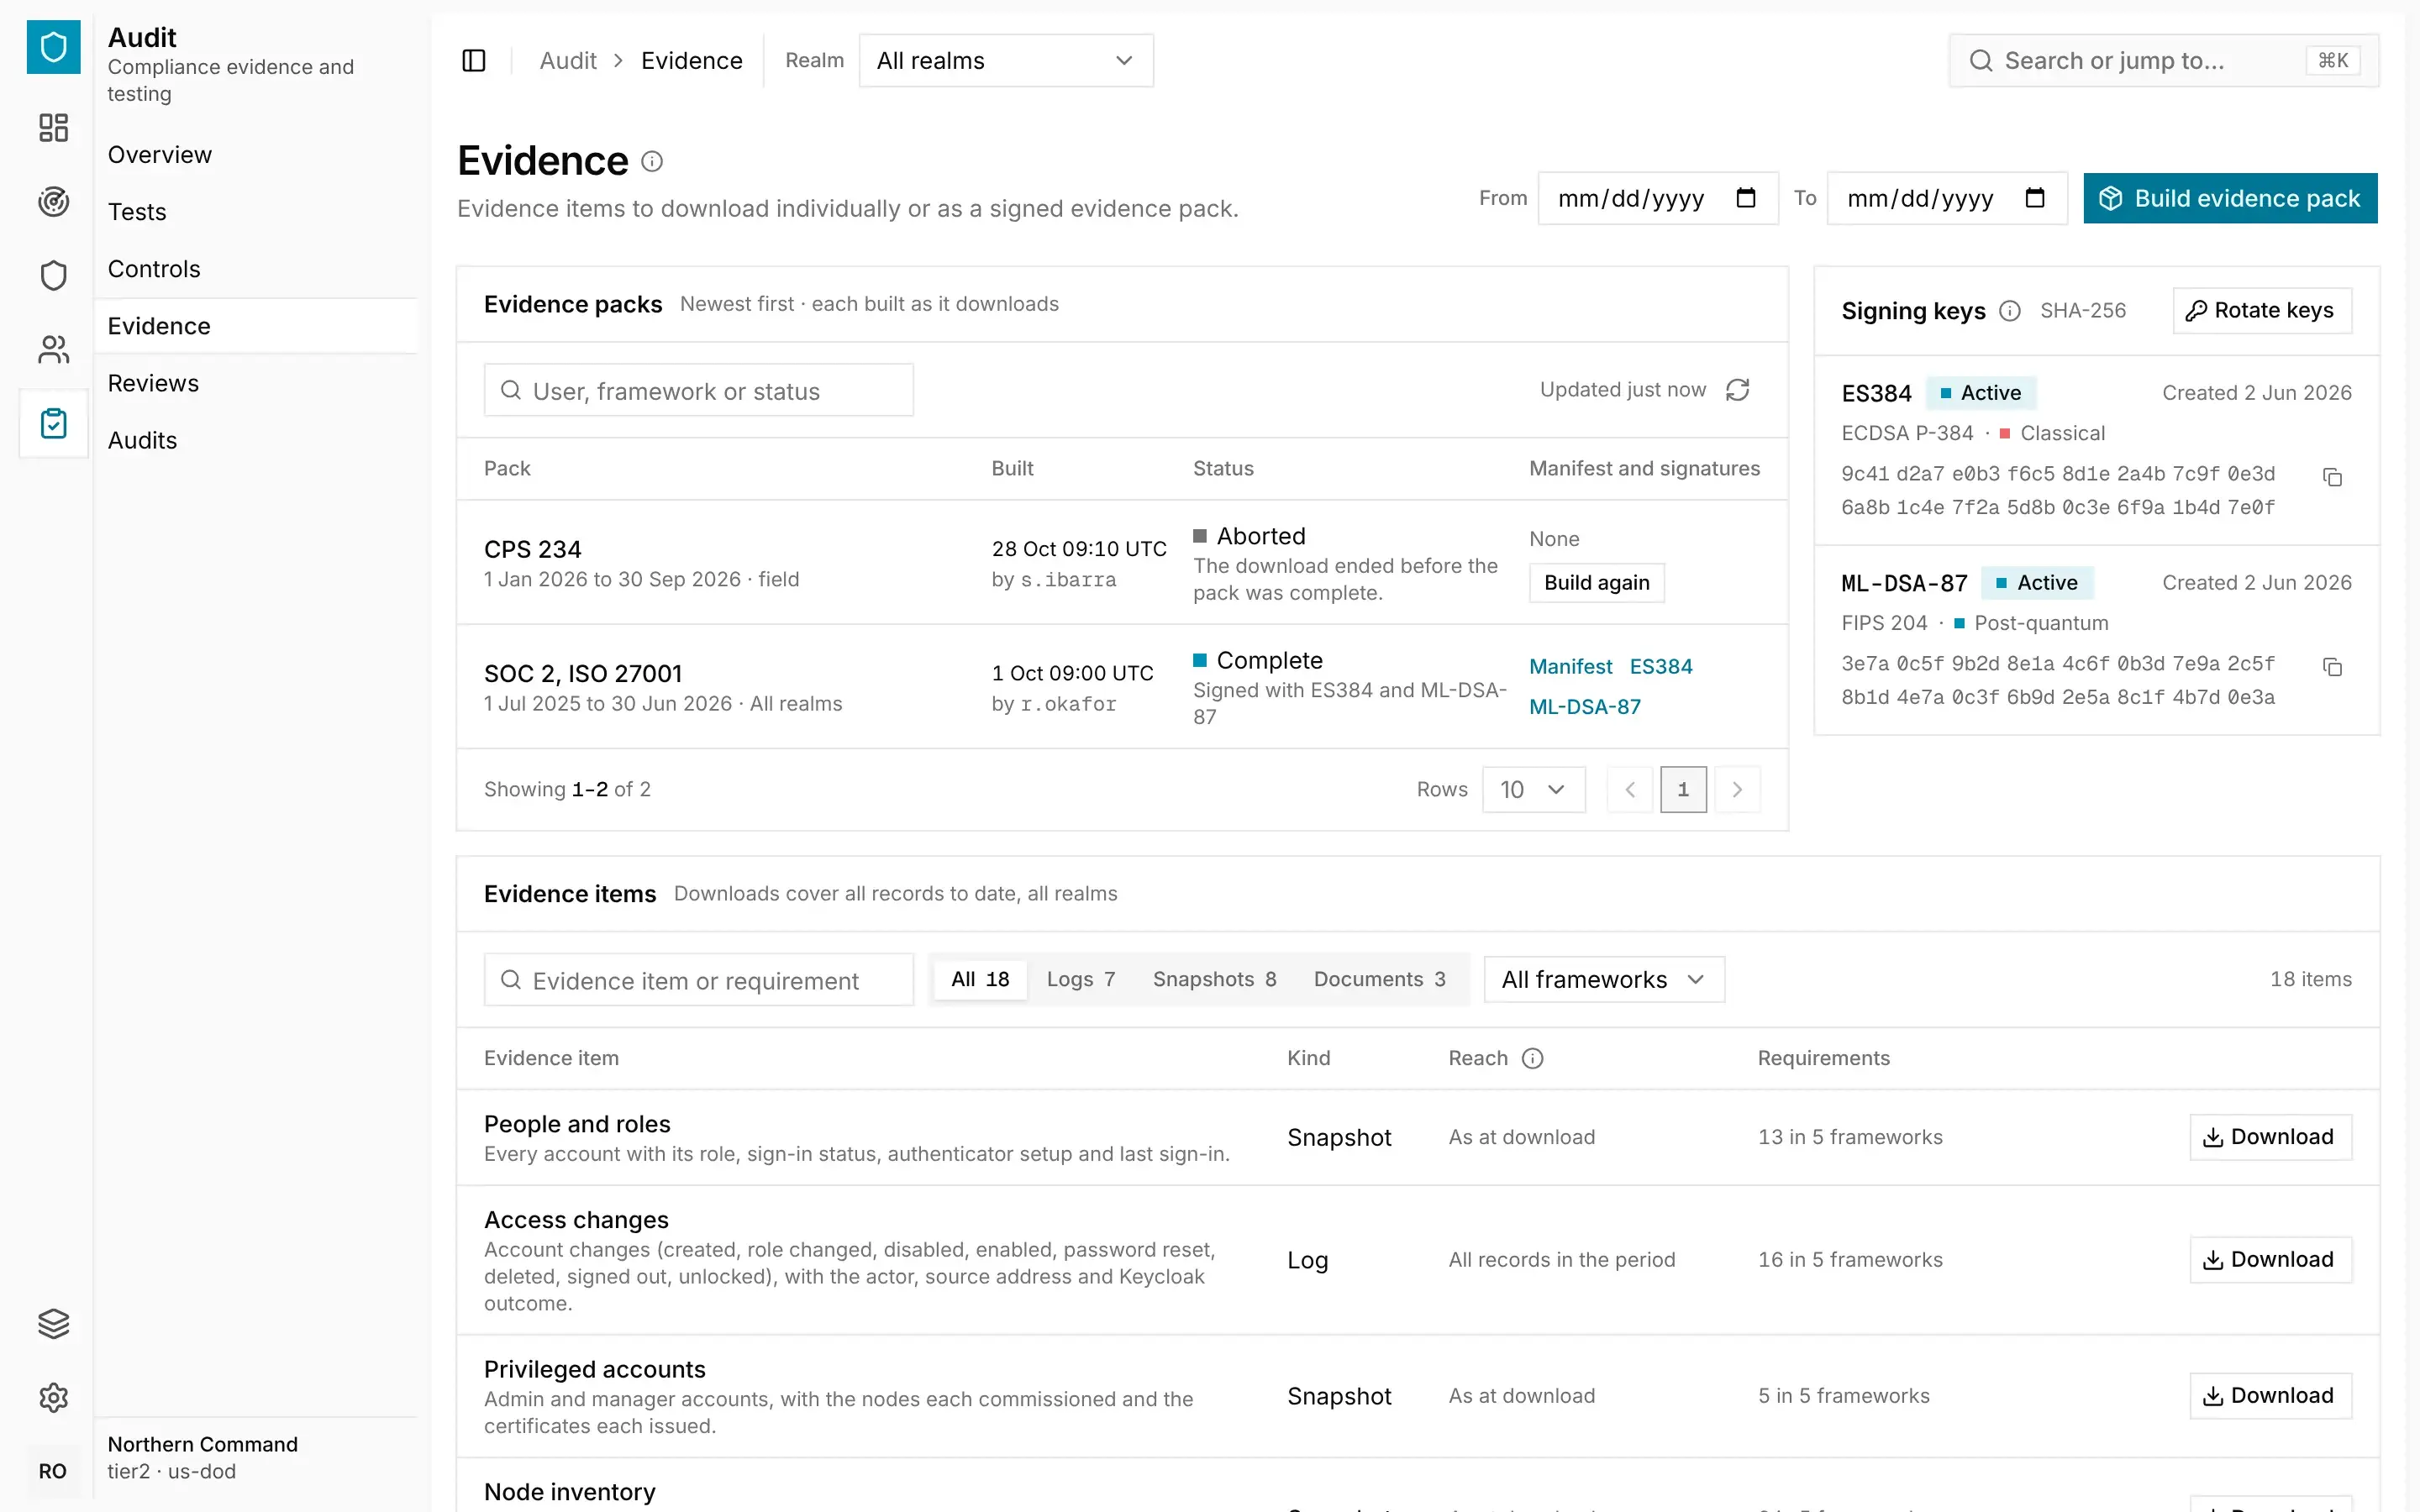
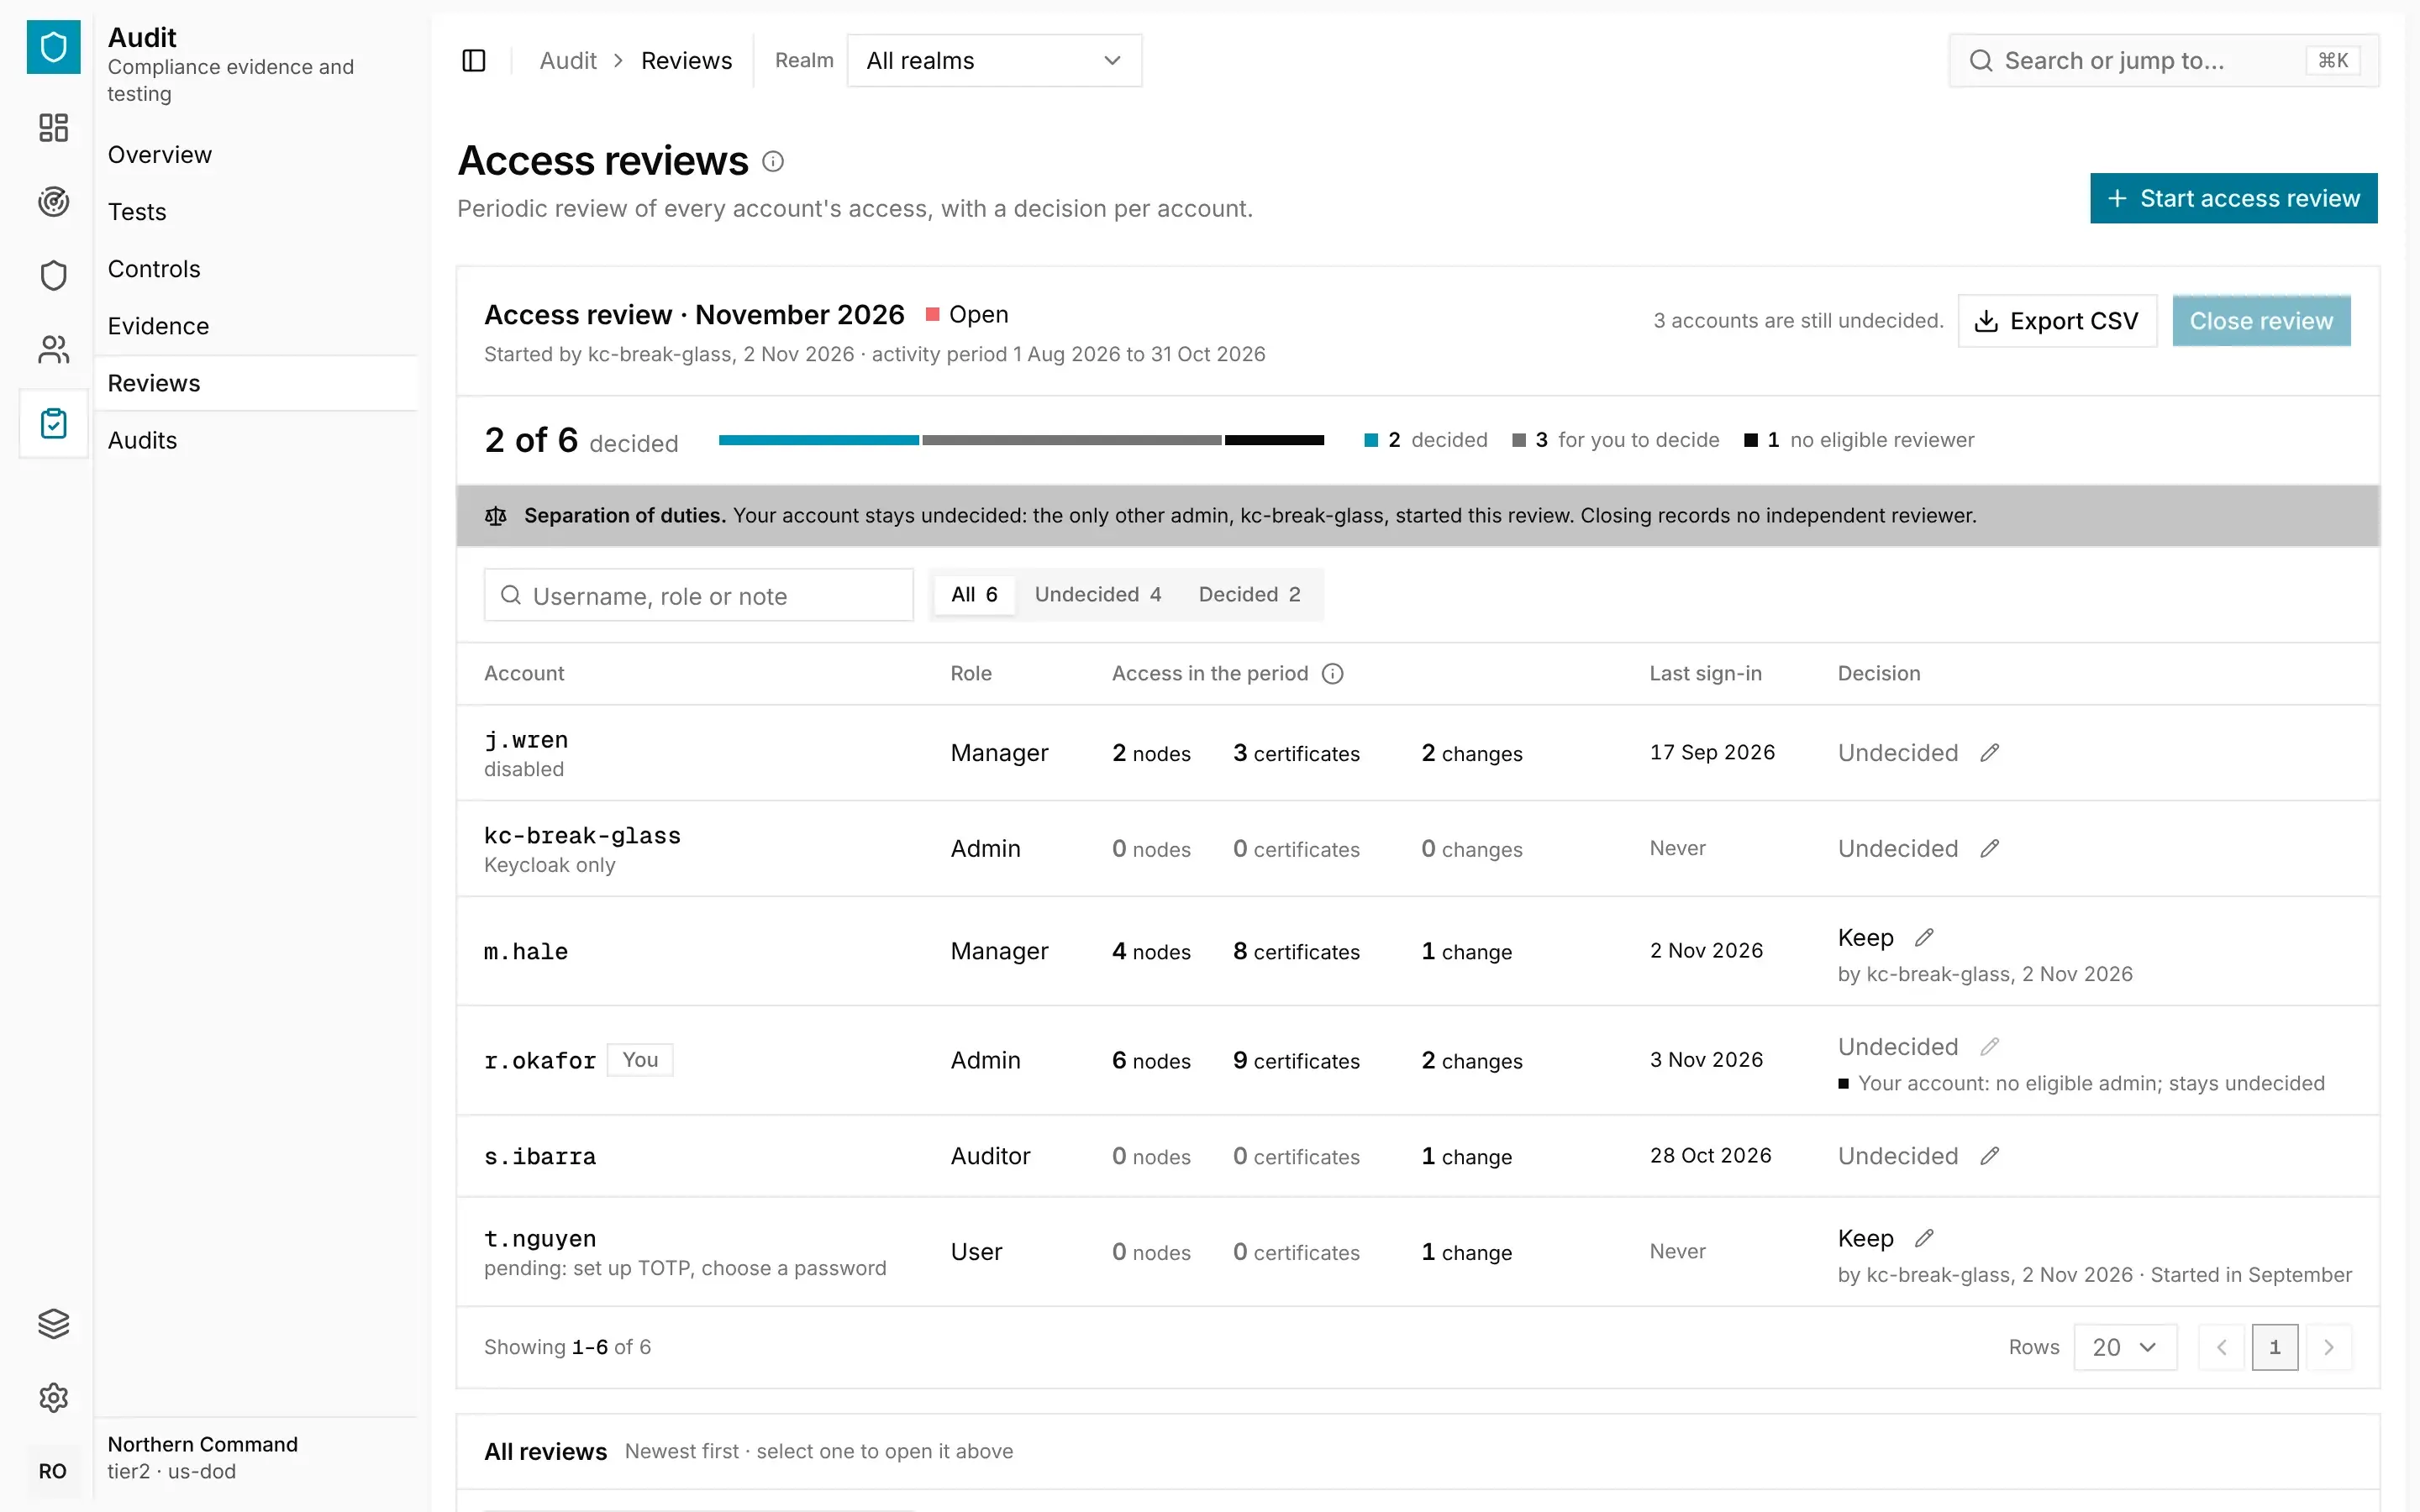
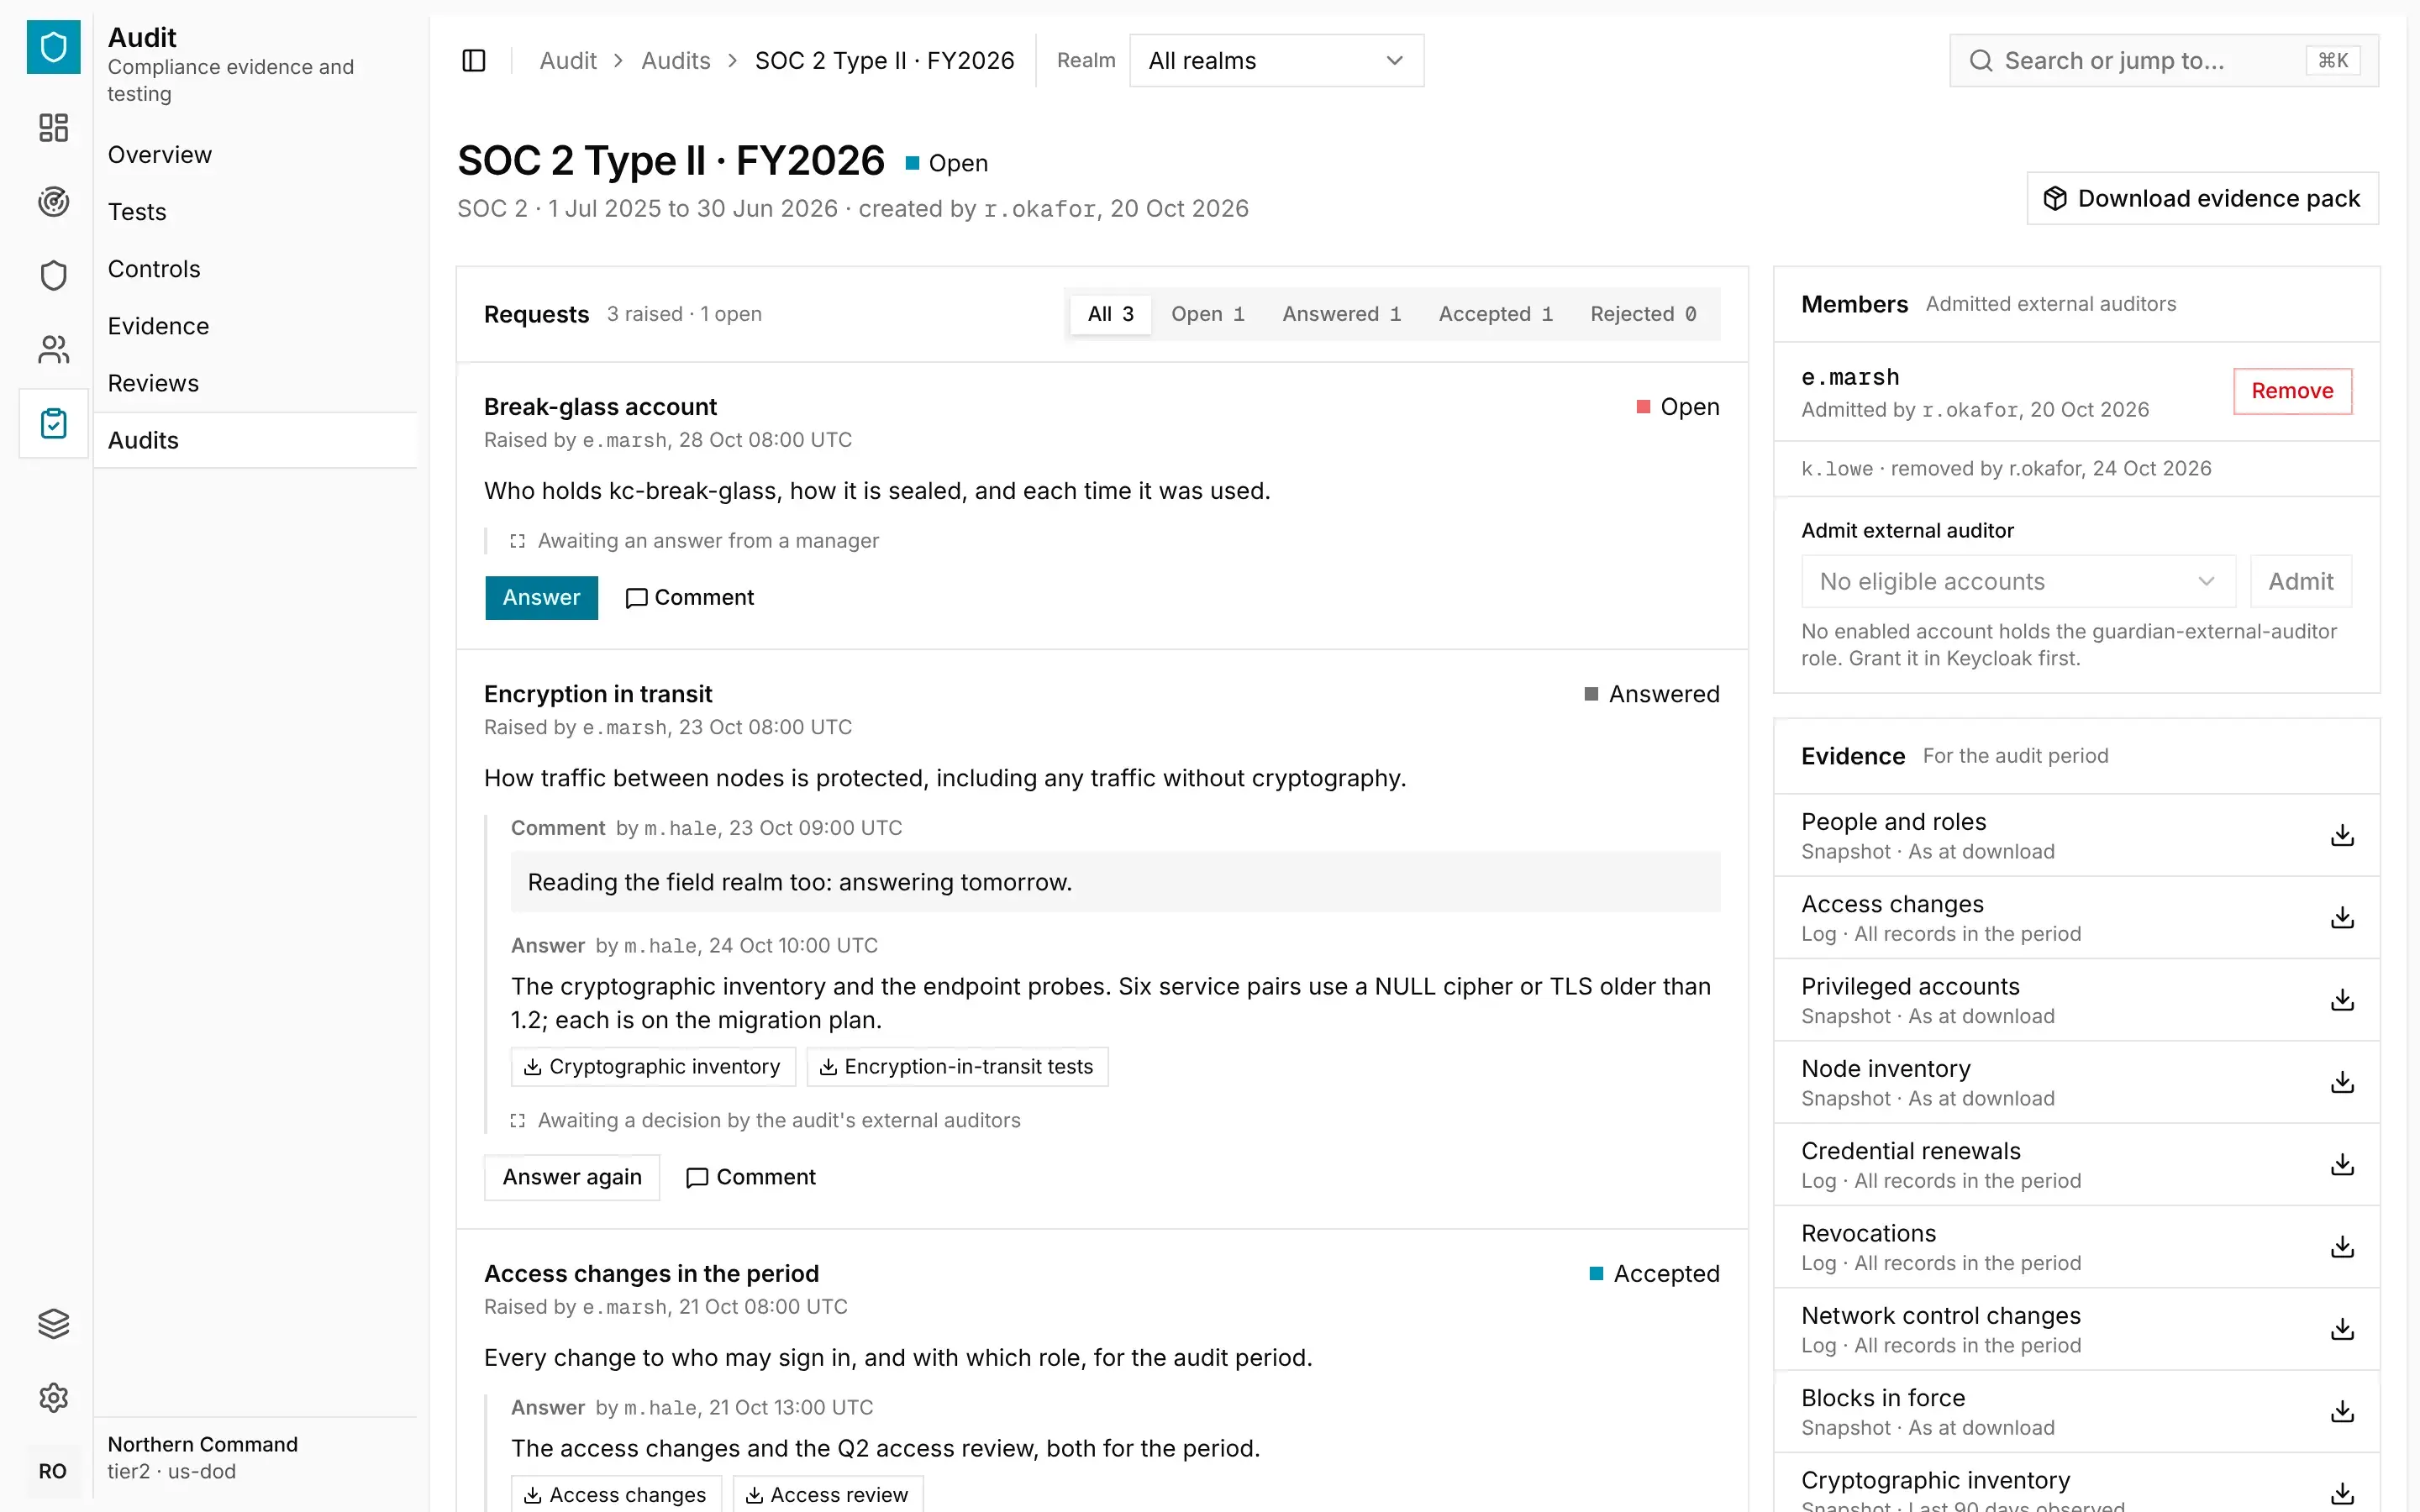
Your posture across six frameworks: failing tests first, access reviews in progress, open auditor requests and recent evidence packs.
Six frameworks, mapped requirement by requirement.
A mapping for your compliance team to review and adopt. Each requirement lists the evidence and tests that support it, and any known gaps.
- Trust Services CriteriaThe 2017 criteria with the 2022 revised points of focus, mapped criterion by criterion. All 33 common criteria are accounted for, including those your organisation evidences itself.
CC6.1 · access is limited to identified and authenticated people and nodes - Annex A controlsThe 2022 edition, mapped control by control. All 93 Annex A controls are accounted for, including those your organisation evidences itself.
5.18 · access rights are granted, reviewed and removed - Information security and operational riskCPS 234 and CPS 230, mapped section by section to match how APRA-regulated entities structure their own mappings.
CPS 234 · control effectiveness is tested and weaknesses are reported - Guidelines by topicThe 2026 ISM guidelines, mapped by guideline topic so the mapping stays stable as control numbers change each quarter.
cryptography · approved cryptography protects data in transit - Revision 5 controlsMapped control by control, consistent with the guardian's own compliance documentation.
AC-2(4) · account management: automated audit actions
Test, collect, review, respond.
- Automated control testsHourly checks such as no connections using NULL ciphers or TLS older than 1.2, no nodes on expired credentials and every CA signing with ML-DSA. Each test has an owner, a deadline and an exact failure history.
- Signed evidence packsEvery evidence item a framework requires for the period, bundled with the known gaps in one archive. The manifest is signed with ECDSA P-384 and ML-DSA-87 using keys sealed in the guardian.
- Access reviewsPeriodic reviews of every account, with a keep, change or remove decision recorded for each. No one reviews their own access.
- Auditor workspacesExternal auditors see only their audit's period and frameworks, raise requests and accept or reject responses. The full history is retained.
Need expert support for your migration?
Our engineers can assess your cryptography, design the transition and validate it with your team, through to audit. Talk to us about consultancy.